Choose your DPO from a curated marketplace.
Independent Data Protection Officers across the EU, the UK and Switzerland, each vetted and profiled by our team. Filter by country, industry and the services you need, compare who fits, and appoint them under GDPR Art. 37–39. Every DPO sets their own services, terms and price.
Do I need a DPO?
Art. 37 is mandatory in three cases, plus one you'll feel in diligence.
Most teams discover the requirement during a DPA audit or a customer security review. We'd rather you discover it on a 10-minute call. Tick what's true.
Awaiting input
Tick what's true — we'll classify you.
A DPO is required when any of the three Art. 37(1) triggers apply. Outside those, it's often contractually required anyway — most enterprise-security reviews in 2024–25 ask for a named DPO regardless of legal obligation.
The catalogue
We vet every DPO.
Each one in the marketplace is independent, and none is listed until we have checked their background, the industries they work in, the certifications they hold and the services they sell.
You read them side by side and choose, by jurisdiction and by the work you need doing, monthly or one-time. Nobody is assigned to you.
We will walk you through the catalogue and help you find the DPO who fits your company.
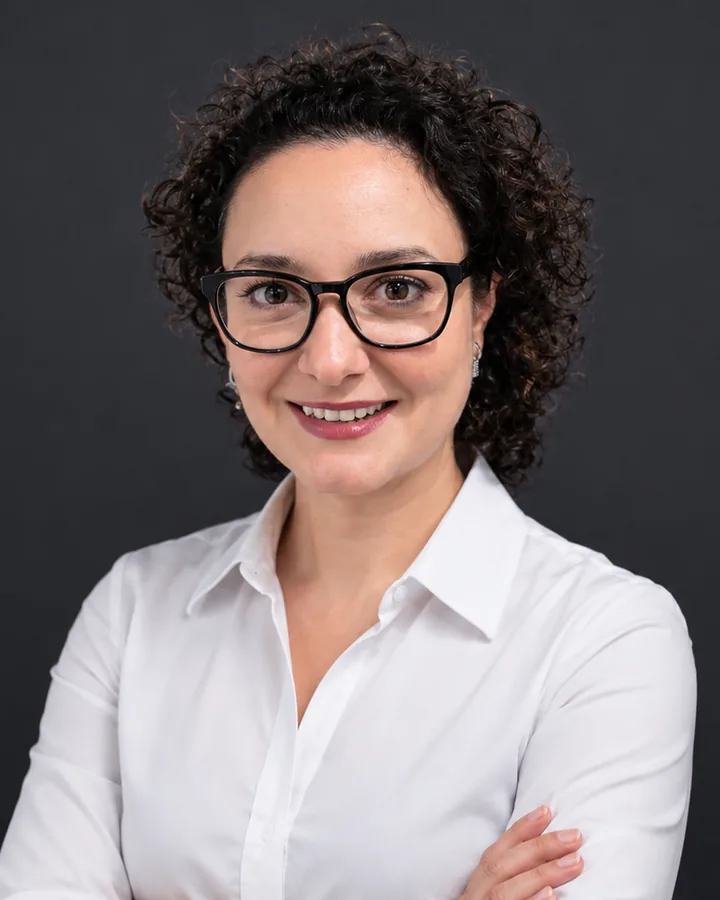
Olga Nielsen
Denmark & Switzerland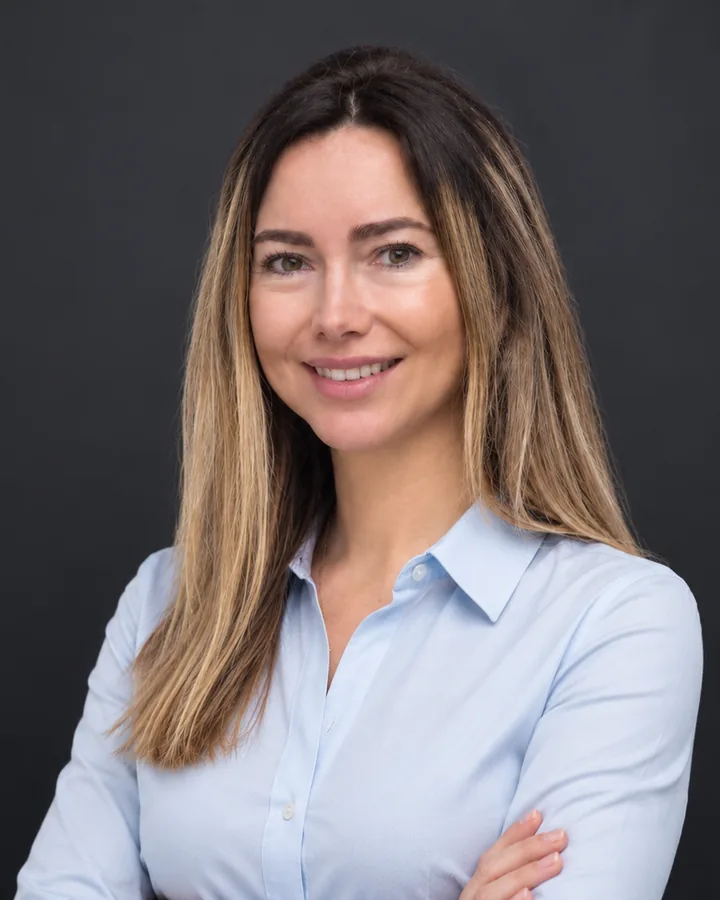
Lucinda Capel
United Kingdom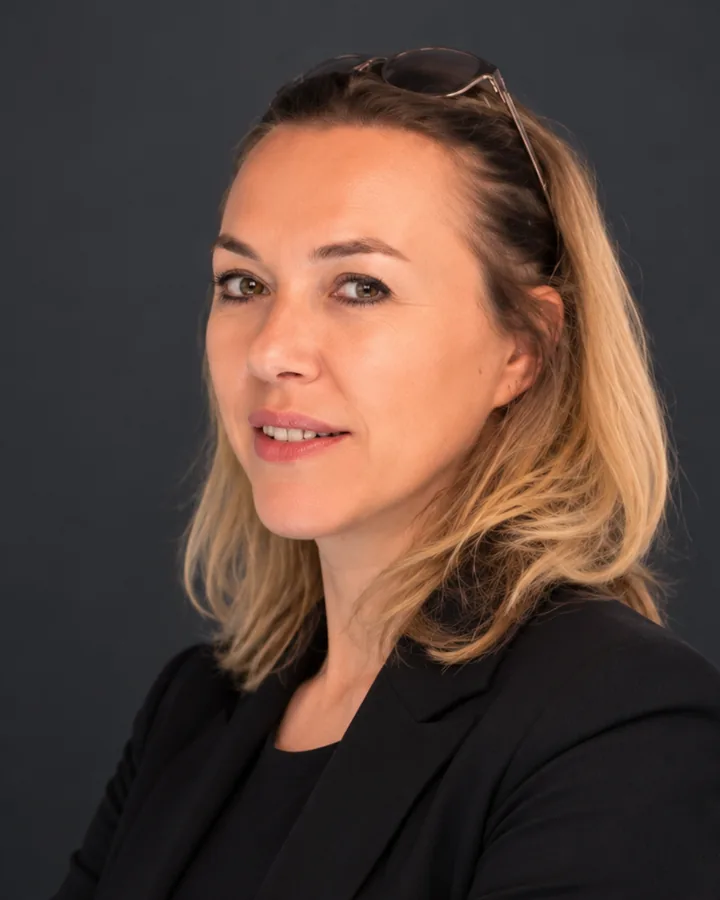
Claire Robinson
United KingdomA selection from the catalogue. The full list, each DPO's services and their prices are in the platform.
What a DPO does — and doesn't
The statutory role, done well. No scope creep.
In scope Art. 39
- Advise on GDPR, UK GDPR, ePrivacy obligations, and national add-ons
- Monitor compliance — audits, staff training, accountability
- DPIA review, risk sign-off, prior consultation with the DPA (Art. 36)
- Cooperate with and act as contact point for the supervisory authority
- Data subject point of contact under Art. 38(4)
- Report directly to the highest management level — written, board-ready
- Incident & breach advisory, including Art. 33 / 34 notification drafts
- Vendor DPAs, transfer mechanisms (SCCs + TIA), sub-processor register
Out of scope By design
- Determining purposes and means of processing — stays with your controllers. Independence is mandatory.
- Litigating on your behalf — a DPO briefs and coordinates with external counsel, but does not act as barrister
- Building your privacy engineering stack — they advise on requirements; your engineers build
- Managing your security program — CISO-adjacent, but a distinct role
- Contractual privacy negotiation with every customer — expect a playbook and help with the hard ones, not a seat at every call
The boundary matters. Under Art. 38(6), the DPO must not face a conflict of interest with other tasks. Each DPO sets their own scope beyond Art. 39, and it is written into the services you buy from them.
How it works
Browse, choose, pay once — they join your workspace.
- Browse the catalogue
Search by name, specialty or certification, or narrow by country, vertical and service. Each profile carries the DPO's background, the industries they work in, their services and their starting price.
- Pick the services you want
Services are grouped monthly and one-time, and you can mix both. Review the total before anything is charged, and send a first message with the order if you want to. One purchase covers one DPO.
- They accept and join
Once you pay, the DPO is invited to your workspace and the conversation for each service opens. When they accept, they become a member with the DPO role. If they decline, every service ends, billing stops and we refund you — then you choose someone else.
- Publish their details
Article 37(7) asks you to publish your DPO's contact details and tell your supervisory authority. Agree with your DPO which details to use — your Privacy Center's privacy contact is the usual place — and they can advise you on the filing itself.
What you publish under Art. 37(7)
// Your privacy policy, and the notice
// you send your supervisory authority

Data Protection Officer
<your DPO's name>
c/o <your company>

Email: dpo@yourcompany.com

// Yours to publish and to notify.
// Hiring through EU Presence does not
// file the designation for you — your
// DPO can advise you on how.
The obligation sits with the controller, which is you. What you get from the marketplace is the person to name, and someone who has done it before.
Pricing
Pick the right DPO for your company.
Data Protection Officer
An outsourced GDPR Data Protection Officer under Articles 37–39. Browse the vetted DPOs on our marketplace and pick the one whose scope and rate fit. Each DPO sets their own services, terms and price.
True of every engagement
- A named DPO appointed under Art. 37
- Your DPO's advice on the Art. 37(7) details you publish and notify
- Art. 38 independence, free of conflicts of interest
- The statutory tasks of Art. 39, which the regulation defines
- A vetted shortlist — you choose, we do not assign
- Their rate published before you commit, never hourly
- One contract and one invoice, through EU Presence
Everything past the statutory role — DPIAs, keeping your records of processing, training, response times, the channels they work in — is each DPO's own offer, on their own terms and at their own price. Compare them on the marketplace and pick the scope that fits.
This is on top of your platform plan, which starts at $0. See every price →
Often purchased together
The standard privacy foundations stack.
Common questions
What GCs ask first.
Is an outsourced DPO actually allowed under GDPR?
Yes, explicitly. Art. 37(6) permits the DPO to be "a staff member of the controller or processor or fulfil the tasks on the basis of a service contract." The EDPB guidance confirms this is a first-class option and specifically endorses it for SMEs and non-EU companies without local privacy staff.
What's the difference between a DPO and an Art. 27 Representative?
Different roles, often confused. A DPO (Art. 37–39) advises you on compliance — internal-facing. A Representative (Art. 27) is your legal EU-side contact for authorities and data subjects. If you have no EU establishment you may need both. EU Presence acts as your representative itself; the DPO you hire from the catalogue is independent of us.
Does our DPO have access to confidential information?
Yes — and they're bound by statutory confidentiality under Art. 38(5). A DPO you hire joins your workspace with the DPO role, which sets what they can see. Your own confidentiality policy and code of conduct apply on top.
How does the DPO stay independent if we're paying them?
The structure matters. The DPO reports to your highest management but receives no instructions on how to perform the role (Art. 38[3]). Every DPO in the catalogue is independent — they are not our employees, they set their own terms, and they can only be dismissed for cause.
What happens if a regulator opens an investigation?
Your DPO is the point of contact under Art. 39(1)(e). What that means in practice — response times, drafting, who they bring in when it escalates — is part of the services you agreed with them, so read those before you buy rather than after.
Can we switch DPOs mid-engagement?
Yes. Each monthly service is its own subscription, so you end the ones you no longer want in Settings and choose another DPO from the catalogue. Arrange the handover with both of them, and remember to update the contact details you published under Art. 37(7).
Find the DPO who fits.
Independent DPOs across the EU, the UK and Switzerland, profiled so you can compare them. Filter by country, industry and service, pick the one you want, and pay for only the services you need.